ISMS software from Germany for ISO 27001, NIS2 and TISAX
Flux ISMS brings asset inventory, risk management, controls, evidence and audits together in one information security management system – built in Munich, GDPR-compliant and hosted in Germany.
- Hosted in Germany
- ISO 27001 · NIS2 · TISAX · SOC 2 · GDPR · DORA
- Auditor portal included
- From €54 per user/month
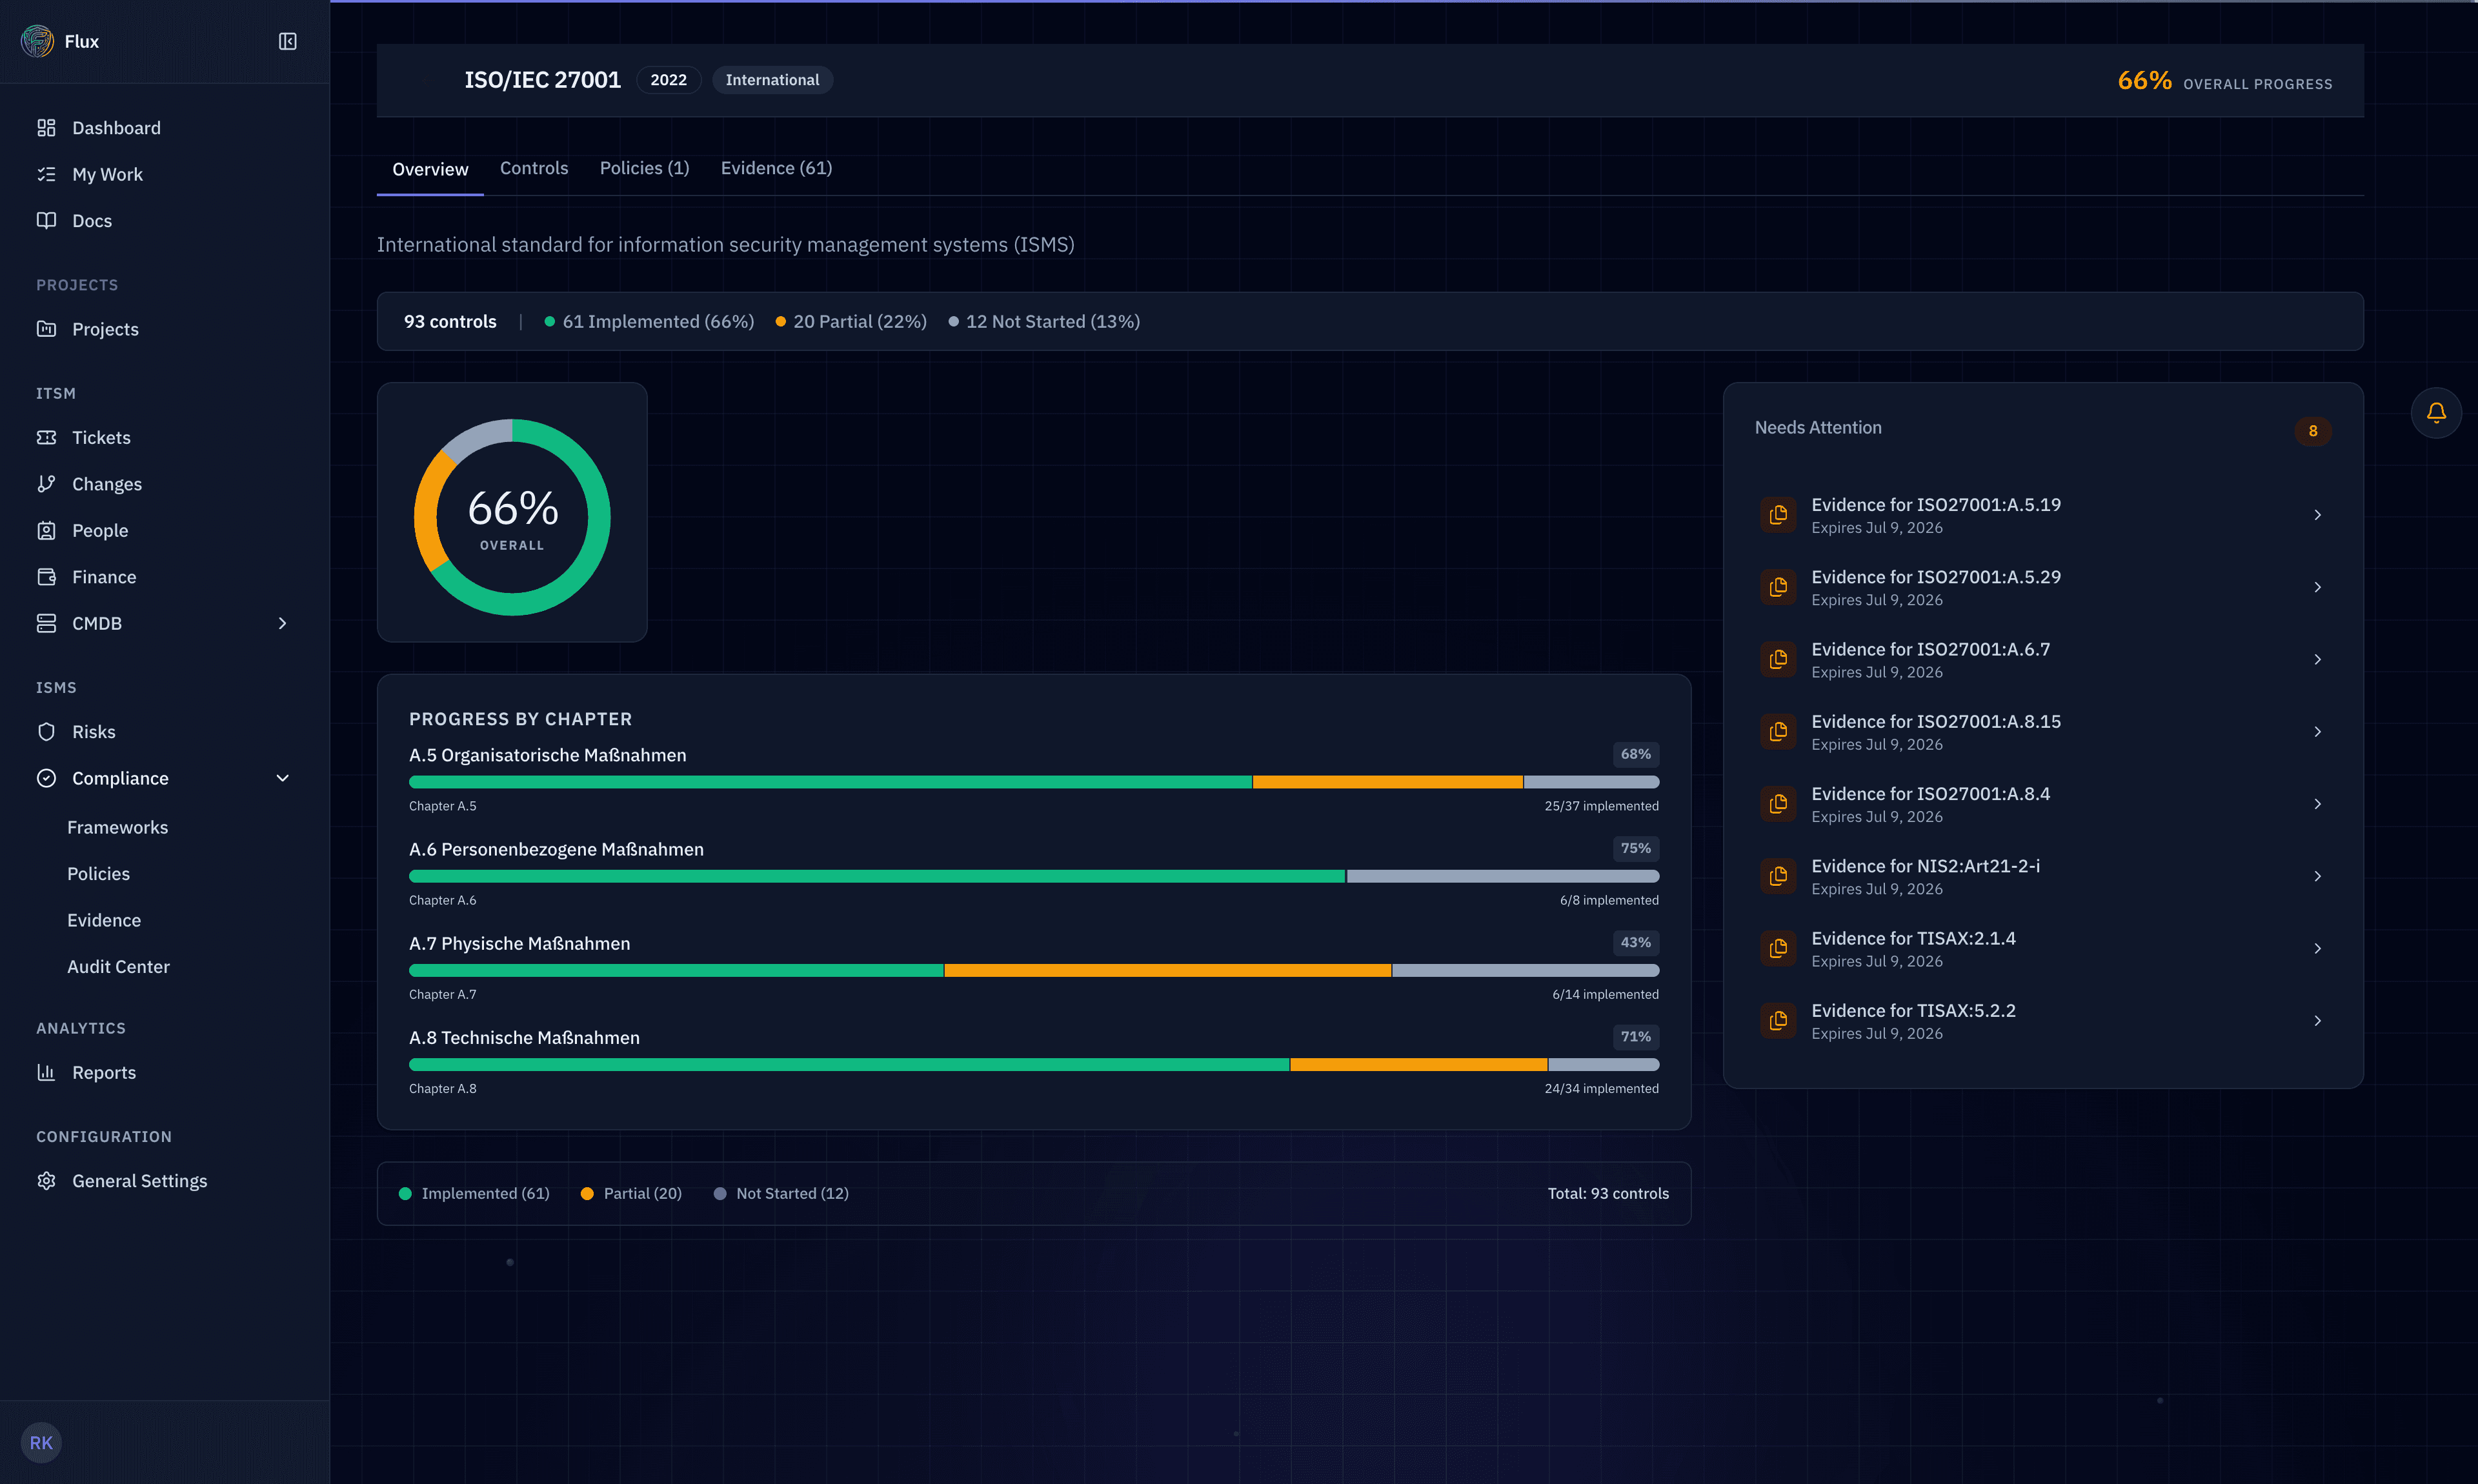
What is ISMS software?
ISMS software is a tool for building and operating an information security management system (ISMS) in line with ISO/IEC 27001 or comparable standards. It replaces scattered spreadsheets and document templates with a central system for scope, asset inventory, risk assessment, controls, the Statement of Applicability, evidence, internal audits and management reporting – keeping the ISMS plan-do-check-act cycle demonstrable at all times.
For companies covered by NIS2, such a management system is the usual way to document the required risk management measures and to prove them to management, auditors and supervisory authorities.
Why Flux as your ISMS tool?
Six reasons information security officers, CISOs and compliance teams in mid-sized companies choose Flux ISMS.
Hosted in Germany, built in Munich
Runs on ISO 27001-certified Hetzner infrastructure in Germany with EU data residency and GDPR-compliant processing. Development, hosting and support come from one team – with a direct line to the founders.
Evidence-based compliance score
A control only counts as implemented once an approved piece of evidence exists. Drift detection flags when policy and infrastructure diverge – instead of claiming compliance with a checkbox.
One control set for multiple frameworks
Implement controls once and map them to ISO 27001 (93 Annex A controls), NIS2, TISAX, SOC 2, GDPR and DORA. Every piece of evidence counts for all affected frameworks at the same time.
Automated evidence collection
Recurring evidence is collected automatically from Microsoft Intune, Entra ID and Action1, given an expiry date and queued for renewal – with a growing catalog.
Auditor portal without extra accounts
External auditors get read access to controls, evidence and findings via magic link. Audit findings flow straight into corrective action plans (CAPs) with owners and deadlines.
ISMS, CMDB and service desk on one data model
Risks attach to real assets from the CMDB with CIA classification, and security incidents from the service desk can create risks directly. No export-import between GRC tool and IT operations.
All ISMS modules in one package
Flux ISMS includes these specialist modules for information security and compliance – each with its own detail page.
RisksRisk Management
Risk register with heat maps and AI-assisted detection.
View moduleComplianceCompliance & Audit Management
Controls mapped to ISO 27001, NIS2, TISAX, SOC 2, and more.
View moduleVendor RiskThird-Party Risk Management
Third-party assessments tiered by criticality and data sensitivity.
View moduleBusiness ContinuityBusiness Continuity Management (BCM)
Continuity plans, RTO/RPO objectives, and tested disaster recovery.
View moduleTrainingSecurity Awareness Training
Track training assignments, completion, and recertification.
View moduleEvery package also includes the seven core modules: Approvals, Tasks, CMDB, Wiki, People, Discovery, and Billing.
Standards and regulations Flux ISMS covers
Control mapping, evidence collection and audit management for the frameworks that matter in the German and European market.
- ISO/IEC 27001:2022
- Certifiable standard for information security management systems – 93 Annex A controls, Statement of Applicability, internal audits.
- NIS2 / BSIG
- Risk management measures under Section 30 of Germany's BSI Act, evidence for business continuity (Art. 21(2)(c)) and training (Art. 21(2)(g)), reporting processes.
- TISAX
- The automotive industry's assessment and exchange mechanism based on the VDA ISA catalog – for suppliers and service providers.
- SOC 2
- Trust Services Criteria for security, availability and confidentiality – relevant for vendors with US customers.
- GDPR
- Technical and organizational measures (Art. 32), records of processing as an evidence base, supplier assessment.
- DORA
- Digital operational resilience in the financial sector – ICT risk management, third-party risk and testing.
Spreadsheets, compliance automation or Flux ISMS?
Where Flux sits compared with the two most common alternatives in the mid-market.
| Spreadsheets & file share | Pure compliance automation | Flux ISMS | |
|---|---|---|---|
| Risk register with workflows | Manual, no history | Usually available | Assessment, treatment, approval, history |
| Asset inventory (CMDB) | Separate list | Often cloud inventory only | Full CMDB with auto-discovery included |
| Evidence | File storage | Automated, mostly US-cloud focused | Automated from Intune, Entra ID, Action1 – plus manual evidence |
| Hosting & data residency | Your own infrastructure | Typically US vendors | Germany (Hetzner), EU data residency |
| Price | Staff time | Often from €10,000/year, quote only | From €54 per user/month, bookable online |
| Link to IT operations | None | Via integrations | Service desk, changes and CMDB in the same system |
Simplified positioning of typical tool categories as of 2026 – not a comparison of individual vendors.
Transparent pricing, bookable online
Flux ISMS costs €68 per user per month (€54 billed yearly) – including the complete core platform with CMDB, discovery and wiki. A team of three starts below €2,000 per year.
Requesters are always free. 14-day free trial with 2 seats – cancel anytime.
Frequently asked questions about ISMS software
What is the difference between ISMS software and GRC software?
ISMS software focuses on building and running an information security management system per ISO 27001: assets, risks, controls, evidence, audits. GRC software (governance, risk and compliance) takes a wider view including enterprise risk, policy management and third-party risk. Flux ISMS covers both – the Vendor Risk module, policy versioning and the risk register are part of the package.
Is Flux ISMS suitable for mid-sized companies?
Yes. Flux ISMS is designed for organizations with 50 to 1,000 employees that want to build an ISMS without a large consulting project. There is no minimum purchase beyond two seats, pricing is public and booking happens online. Requesters – for example employees who provide evidence or submit tickets – are free.
Where is the data hosted?
Flux runs on ISO 27001-certified Hetzner infrastructure in Germany; Cloudflare acts as a protective layer in front of the application. Data is encrypted at rest with AES-256-GCM and in transit via TLS. The operator is starnode solutions GmbH, based in Munich.
Which frameworks does Flux ISMS support?
ISO/IEC 27001:2022, NIS2 (German BSI Act), TISAX, SOC 2, GDPR, DORA and CCPA. Controls are implemented once and mapped to all activated frameworks; every piece of evidence counts for all affected controls at the same time.
How quickly is Flux ISMS ready to use?
Typical path: day 0 tenant and SSO via Microsoft Entra ID, day 1 automatic asset discovery from Azure, AWS, Hetzner and M365, day 3 ISO 27001 controls mapped with drift detection active, day 7 first exported evidence pack. A 14-day trial with the full feature set is free.
Can I use Flux ISMS without the ITSM modules?
Yes. Flux ISMS is a standalone package with all seven core modules plus risk management, compliance & audit, vendor risk, business continuity and training records. The service desk and change management are added with Flux Complete – you can switch at any time.
Build your ISMS before the audit is due
14-day free trial – all modules, 2 seats, no charge before the trial ends.
You might also like: ITSM Software